Can Anyone Else Read My Notes? The Honest Answer
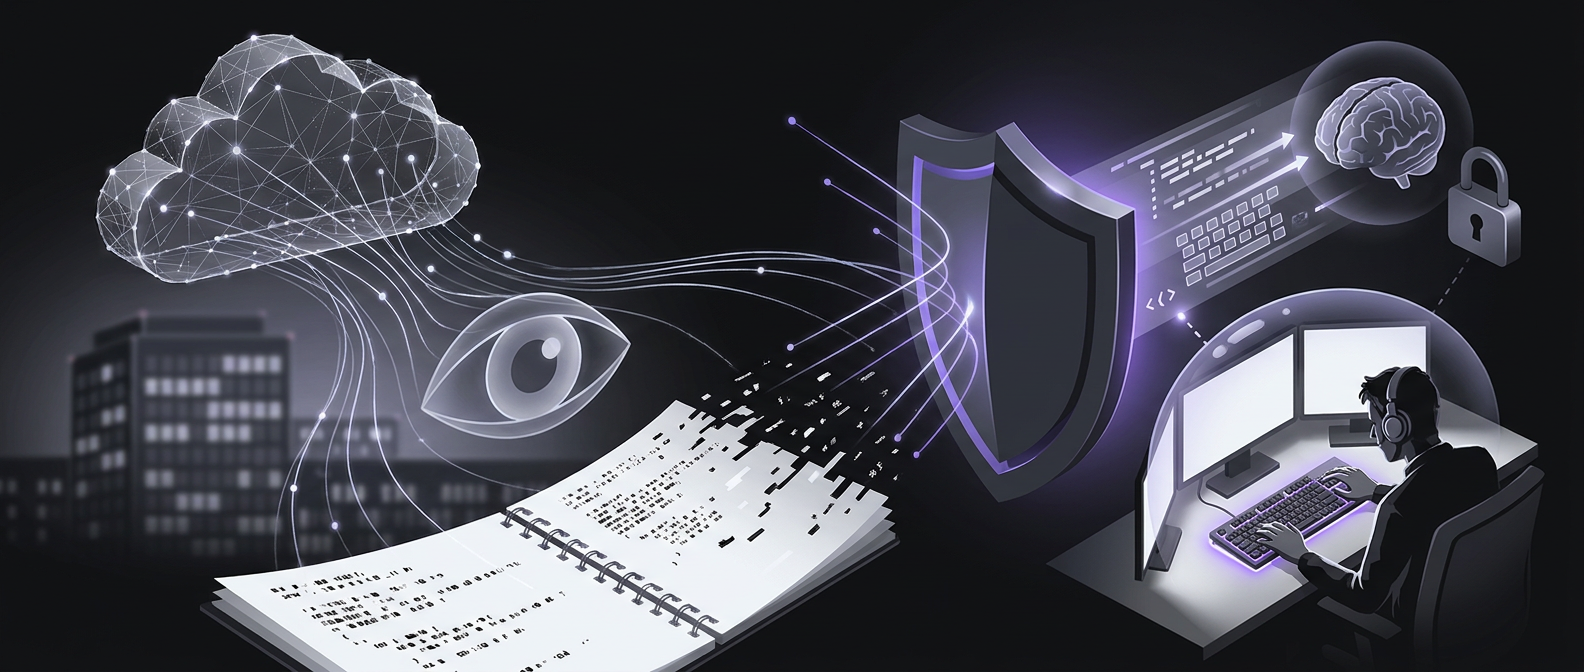
The honest answer is that in most popular apps, yes, the company, a rogue employee, or a sophisticated attacker can read your notes. In a zero-knowledge, client-side encrypted app like SimplyBoard, the answer is a definitive no. Unless someone physically holds your unlocked device or knows your master password, your data is mathematically unreadable to everyone, including the developers.
It is the question that quietly sits in the back of every privacy-aware person's mind when they open a notes app. If someone really wanted to · a government agency, a hacker who breached the database, or an engineer with high-level access · could they read this? The answer depends entirely on one technical detail most apps avoid talking about: who holds the encryption key.
Private is not the same as encrypted
Companies love the word "private." It sounds reassuring, but it often describes a policy, not a technical reality. When a service provider says your data is private, they are usually promising not to look at your data and promising not to sell it. This is a legal agreement, and legal agreements have loopholes.
Policies can change. Employees can break them. Governments can override them with subpoenas. Attackers can ignore them entirely once they gain access to the server. "Encrypted" means something stronger, but even then, you must ask *where* it is encrypted. If the company encrypts your data on their servers (encryption at rest), they still hold the keys. They are essentially locking your front door but keeping a master key in their office.
True security requires client-side encryption. This means the data is mathematically scrambled on your device, and only someone with your specific key can unscramble it. If the company does not have the key, the company physically cannot read your notes, no matter who asks.
Who can read notes in a typical "private" app
If you use a standard cloud-based notes app that does not specify "zero-knowledge" or "end-to-end" encryption, the following groups can technically access your content:
- Engineers with production database access: While usually restricted, senior developers often have tools to view raw database rows for troubleshooting.
- Support staff using admin tools: Many "private" apps allow support agents to "impersonate" or view user accounts to help solve tickets.
- Hackers who breach the server: If the database is stolen, and the company holds the keys, the hacker can eventually decrypt the entire dataset.
- Governments and Law Enforcement: If served with a valid legal request, companies that hold the keys are legally required to hand over your decrypted data.
- Machine Learning Systems: Many modern productivity apps scan user content to train AI models or provide "smart" suggestions.
Where popular apps actually sit
Most household names in the productivity space prioritize convenience over absolute privacy. Apps like Apple Notes, Google Keep, Notion, Evernote, and OneNote store your notes in a form their servers can read.
While Apple Notes offers optional "locked" notes that use end-to-end encryption, the default state for the vast majority of your data in most cloud apps is plaintext on their infrastructure. This is a deliberate tradeoff. By holding the keys, these companies can offer features like:
- Server-side search (searching through gigabytes of notes instantly).
- AI-powered summaries and content generation.
- Rich web previews for links.
- Easy password recovery if you forget your login.
The cost of this convenience is that your data lives on their servers in a readable form. For many users, this is acceptable. For those storing sensitive intellectual property, journals, or command snippets, it is often a dealbreaker.
A smaller group of apps, including SimplyBoard, Standard Notes, and Proton, use what is called zero-knowledge encryption. In these systems, the server only ever sees "ciphertext" · a random string of characters that is useless without your password.
What zero knowledge actually means
Zero knowledge is a precise technical claim, not marketing fluff. It means the operator of the service has no technical ability to read your data, even if they are forced to by a court order. In a robust zero-knowledge system like SimplyBoard, the process looks like this:
- Key Derivation: Your password is never sent to the server. Instead, it is put through a memory-hard function called
Argon2idon your device. This turns your password into a high-entropy encryption key.Argon2idis the winner of the Password Hashing Competition and is designed to resist GPU-based cracking attacks. - Encryption: Your notes are encrypted using
AES-256-GCM(Advanced Encryption Standard with Galois/Counter Mode) directly in your browser or app. This is the industry gold standard for authenticated encryption. - Transmission: Only the encrypted "blob" is sent to the server.
- Storage: The server stores the blob. It has no idea if that blob contains a grocery list or a secret business plan.
If a court served the company tomorrow, they could only hand over scrambled bytes. If a contractor went rogue, they would see nothing but gibberish. This is why there is no server-side password reset for your content; if we could reset your password, it would mean we have the power to access your data.
Three questions to ask any notes app
If you want a straight answer about whether a notes app can read your data, these three questions cut through the marketing:
- If I forget my password, can you reset it and give me back my notes? If the answer is "yes," they hold a key that can decrypt your notes. That key is a single point of failure.
- Where does encryption happen? If it happens on their servers (at rest), they are protected from outside hackers, but you are not protected from the company itself. It must happen on your device.
- Can you search my notes from a new device before they are downloaded? If a server can search your notes without you being logged in on that specific device, the server can read your notes.
The SimplyBoard approach to privacy
At SimplyBoard, we built the app for people who ship · developers, founders, and creators who need a fast, private alternative to the status quo. Our architecture is offline-first and privacy-first by default.
- We cannot read your notes: Not your titles, not your tags, not your content.
- Client-Side Encryption: Everything is encrypted on your device before it touches our SOC 2, ISO 27001:2022, and GDPR-certified infrastructure.
- No Password Resets: We provide a one-time recovery code during setup. This is the *only* way to recover your data if you forget your password, because we don't have a "backdoor."
- Search-First, Not Spy-First: We offer instant fuzzy search, but it happens entirely on your local device using an encrypted IndexedDB cache.
The tradeoff for this level of security is responsibility. You own your keys. But in exchange, you get the peace of mind that the answer to "can anyone else read my notes" is a simple, honest no.
Why offline-first matters for privacy
Many users looking for private notes overlook the importance of offline-first architecture. In a traditional cloud app, every keystroke is often sent to the server in real-time. Even if the data is encrypted at rest, the "in-transit" period creates a window of vulnerability.
SimplyBoard uses an offline-first approach. Your notes are stored in an encrypted IndexedDB cache on your local machine. When you type, you are interacting with your local database. The sync process happens in the background, sending only the encrypted changes to the server. This means:
- Speed: Search and retrieval are instant because they don't wait for a round-trip to a server.
- Resilience: You can work in a tunnel, on a plane, or in a dead zone.
- Privacy: Your raw, unencrypted data never exists outside of your device's memory and local storage.
The risk of "God Mode" and employee access
History is full of examples where "private" data was accessed by employees. In other tech giants, "God Mode" tools have been used by employees to stalk users or access sensitive information.
When you use a zero-knowledge app, you aren't relying on a company's HR department or their internal access controls. You are relying on the laws of mathematics. Even if every employee at SimplyBoard wanted to read your notes, they couldn't. The data is ciphertext, and the keys are in your head (or your password manager).
Choosing the right tool for your threat model
Not everyone needs zero-knowledge encryption for their grocery list. However, if you are a developer managing API keys, a founder documenting strategy, or a journalist protecting sources, the "honest answer" matters.
If you value convenience and AI features above all else, apps like Notion or Google Keep are excellent. But if you want a secure notes app where you are the only one with the keys, look for the "zero-knowledge" label. SimplyBoard provides that security without sacrificing the speed of a modern, keyboard-first workflow.
· The SimplyBoard Team
Sources
Every figure above was checked against the page it cites · here they are, so you can check them too.
Frequently asked questions
- Can the company that makes my notes app read what I write?
- Most popular notes apps (Notion, Evernote, Google Keep) use server-side encryption. This means they hold the keys and can technically access your data. Only apps using 'client-side' or 'zero-knowledge' encryption, like SimplyBoard, ensure that the service provider has no way to read your content.
- What is the difference between encryption and zero-knowledge encryption?
- Standard encryption (encryption at rest) protects your data from someone stealing a hard drive from a data center. Zero-knowledge encryption protects your data from the service provider itself. With zero-knowledge, the encryption key is derived from your password on your device and is never shared with the server.
- Why can't some private notes apps reset my password?
- If a notes app can reset your password and restore your notes, it means they have the technical ability to access your data. In a true zero-knowledge system, the company cannot reset your password because they don't have your keys. SimplyBoard provides a one-time recovery code as the only way to regain access.
- What specific encryption standards does SimplyBoard use?
- SimplyBoard uses AES-256-GCM for data encryption and Argon2id for key derivation. This happens entirely on your device (client-side). We also use SOC 2, ISO 27001:2022, and GDPR-certified infrastructure to ensure the physical and network security of the encrypted data we store.
- Can I access my encrypted notes while offline?
- Yes, SimplyBoard is designed to be offline-first. It uses an encrypted IndexedDB cache on your device, allowing you to search and edit your notes without an internet connection. Changes are automatically synced to the cloud once you reconnect, using end-to-end encryption throughout the process.
- What metadata can a zero-knowledge provider see?
- In a zero-knowledge system, the server only sees 'blobs' of encrypted data. It does not see your note titles, the text within them, or your tags. The only metadata typically visible is the account email, the size of the encrypted files, and the timestamps of when they were last updated.
Start writing with true privacy
Get Started Free